ComplianceGenii — Compliance Isn't a Checkbox. It's an Output.
Your obligations live in policy documents. ComplianceGenii ingests those frameworks — SOC 2, ISO 27001, your own technical policies — compiles them into the hard ceiling every AI agent must stay within, and turns what your agents actually did into evidence your reviewers can verify — connected governance records in vCon, the IETF standard for conversation evidence, plus signed exports.
What ComplianceGenii Is
ComplianceGenii is the governance, audit, and policy-translation layer of the AgentGenii Suite. It ingests human-readable compliance frameworks (SOC 2, ISO 27001) and technical policies (Rego, YAML) and translates them into a signed "Maximum Surface" — the absolute ceiling of what any agent may ever do for a given principal. PolicyGenii then negotiates and enforces each contract strictly within that ceiling. ComplianceGenii ingests the redacted runtime audit stream, detects violations, and compiles SOC 2 / ISO 27001 evidence. Its differentiator is the shape of that evidence: the AgentGenii Suite can package governance evidence — who asked, under what authority, what was decided, what came back — as vCon-based records, signed for verification, so a reviewer follows one connected record instead of a log hunt. It governs AI agents — not your customers — and never touches a live tool call.
Core Capabilities
- Ingests SOC 2, ISO 27001, and your own policies (PDF, Markdown, Rego, YAML)
- Compiles them into a cryptographically signed Maximum Surface ceiling per principal
- Sets the outer bound PolicyGenii can never exceed — contracts fit inside it, never outside
- Audits the redacted runtime log stream and compiles SOC 2 / ISO 27001 evidence and violation alerts
- vCon-based evidence: governance records can be packaged as signed vCon records and connected for review
- Exports a signed evidence bundle: report, audit CSV, SHA-256 manifest, and an Ed25519-signed PDF certificate
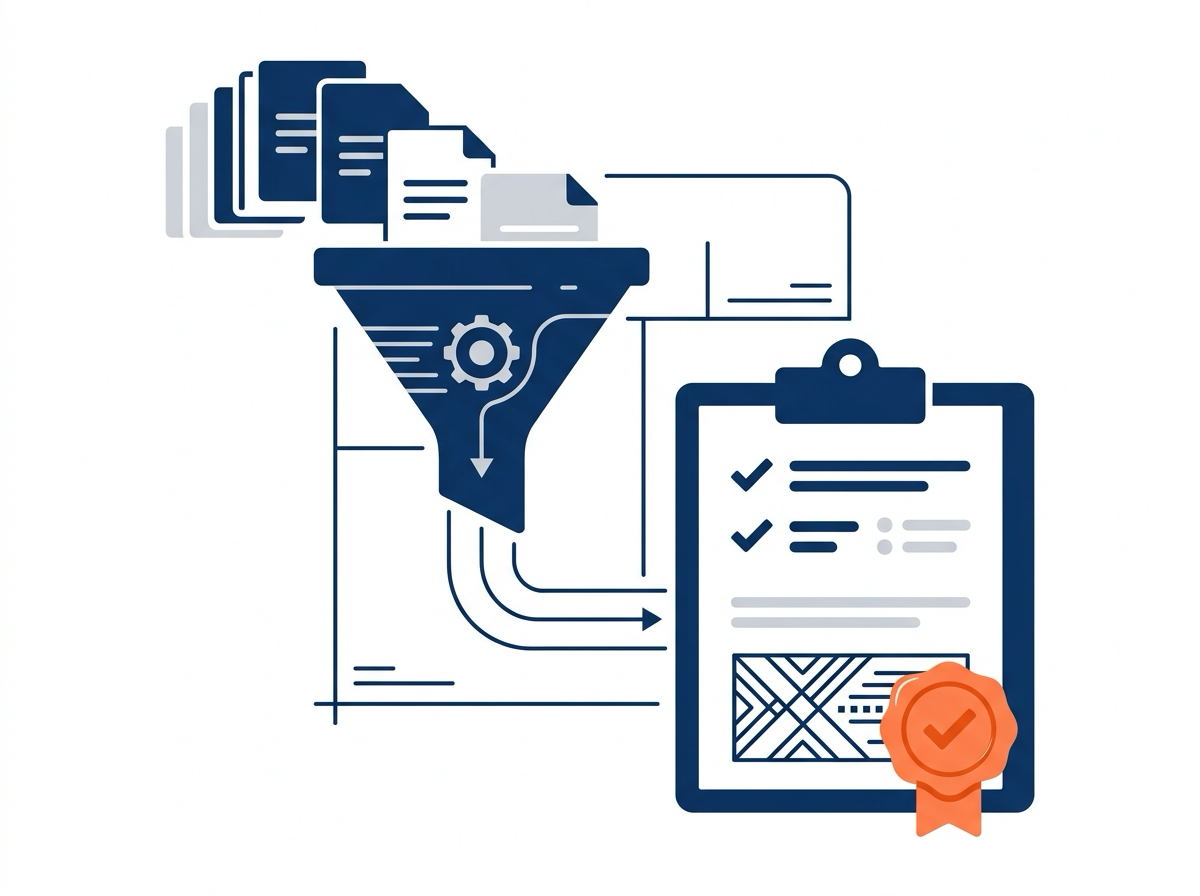
Policy in. Ceilings and audit evidence out.
Frameworks and policy compile into a signed Maximum Surface that bounds every agent, and runtime logs become audit-ready evidence.
- Ingests SOC 2, ISO 27001, and your own policies (PDF, Markdown, Rego, YAML)
- Compiles them into a cryptographically signed Maximum Surface ceiling per principal
- Sets the outer bound PolicyGenii can never exceed — contracts fit inside it, never outside
Built to become your compliance team’s favorite tool.
Less time reconstructing what happened. More time deciding whether the controls worked.
ComplianceGenii brings organizational policy, approval evidence and recorded AI activity into the compliance professional’s workflow. Our ambition is to make it the tool your team reaches for first: when an auditor asks for evidence, when a customer asks how AI is governed, or when an exception needs a defensible answer.
Follow the evidence, from authority to action.
A tool-call log can tell you that something ran. A compliance review asks more: who was accountable, what authority applied, what was approved, what was refused, and what the system reported afterward.
The AgentGenii Suite uses vCon-based evidence to help connect that context. A vCon is a structured conversation record; in this governance setting, it can carry participants, a recorded action, and associated evidence reports. The suite’s implementation can package governance evidence into this representation and sign it for verification.
For your team, the value is a traceable review: connect a recorded event to its decision and authority references, inspect the available supporting material, and verify the record’s integrity. ComplianceGenii’s evidence and completeness views complement that connected record. A signature protects integrity; the review still checks capture coverage, missing records and the actual business outcome.
See how the evidence works- Accountability
- the tenant, acting agent and relevant owner or principal references.
- Authority
- the applicable policy, approval and signed-contract references where recorded.
- Decision
- the action requested and the recorded allow, refusal or escalation context.
- Result
- the reported execution result and any independent upstream confirmation.
- Integrity and coverage
- verification material, reporting period, known gaps and exclusions.
The selected evidence path determines which records and fields are available. vCon evidence, a hashed export bundle and a signed PDF are different representations; the review should identify which it uses.
Evidence for one invoice workflow.
Illustrative review package using synthetic data; this is not a claim that every field appears in one current screen or export.
An accounts-receivable assistant prepares an invoice and requests permission to send it. The reviewer wants to know whether financial access and email delivery stayed within their approved boundaries.
| Review question | Evidence to inspect |
|---|---|
| What work was authorized? | Task and policy references for preparing the selected customer’s invoice. |
| Were financial access and delivery separated? | The financial-read and email-send contracts, their resource constraints, recipient bounds, expiry and call limits. |
| Who approved the send? | The approval record and the reviewer’s authority for that principal and scope. |
| What happened when the recipient changed? | A recorded refusal or escalation, and any separately approved authority used afterward. |
| Was the invoice actually sent? | The governed call’s reported result, reconciled with the email provider’s delivery or acceptance record as appropriate. |
| Can we rely on this package? | Record/signature verification, the covered period, known ingestion gaps and any missing source evidence. |
The review ends with a supported conclusion and explicit exceptions—not merely a green “success” badge. If the workflow requires financial access and email to be mutually exclusive, include evidence of that enforcement control as well; two separate contracts alone do not prove it.
Explore the invoice workflowMake SOC 2 evidence easier to explain.
For teams preparing for SOC 2, AI governance should produce evidence that can be connected to the controls under examination: approved access, accountable changes, monitored activity, exception handling and the protection of information.
ComplianceGenii can help your team organize the AI-governance portion of that review. Start with your control objective, identify the relevant authority and activity records, inspect completeness, and document the conclusion. Your assessment scope determines which Trust Services Criteria are relevant; the categories cover security, availability, processing integrity, confidentiality and privacy. AICPA’s SOC 2 guidance.
The same evidence discipline can support other control programs. For NIST AI RMF work, connect accountability, documented context, evaluation findings and risk responses to the framework’s Govern, Map, Measure and Manage functions. Your team determines the mapping and whether the evidence is sufficient; this is not a claim of automatic framework mapping. NIST AI RMF Core.
ComplianceGenii supports the work of compliance professionals. It does not replace their judgment, an independent examination, or the rest of the organization’s control program.
Ask for a sample evidence reviewBuilt to compose with the rest of Autom8ly’s Genii.
ComplianceGenii sets the outer limits from your policy; PolicyGenii enforces within them at runtime. KnowledgeGenii governs what agents know; CipherGenii keeps data confidential. ComplianceGenii is the governance and evidence layer — it consumes a redacted audit stream after the fact and never sits in the live request path.
Explore Autom8ly solutionsCore Use Cases
Turning SOC 2 / ISO 27001 obligations into enforceable ceilings for every AI agent
Answering an auditor’s question about one AI action with one connected evidence record, coverage stated for the reporting window
Detecting violations from the audit stream — actions without a manifest, shell execution, exfiltration-shaped read/output ratios
Giving compliance reviewers a plain-English, signed view of exactly what each agent is permitted to do